Capabilities — Cybersecurity
Preemptive security for infrastructure, identities and AI
From zero-trust architecture to 24/7 security operations — resilience engineered across your entire estate.
The Challenge
The perimeter is gone and the attack surface keeps growing
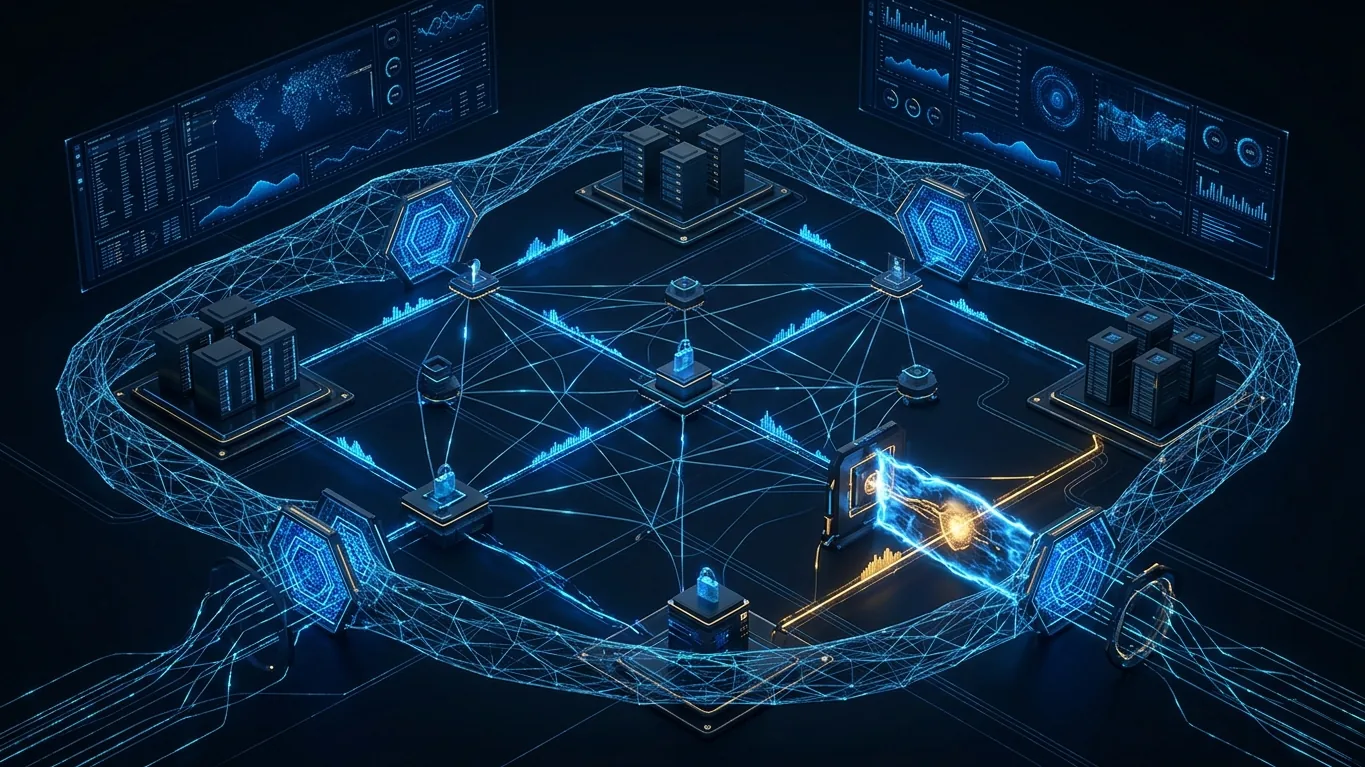
Enterprise security now has to cover multicloud estates, SaaS workflows, CI/CD pipelines, machine identities — and increasingly, AI agents that act on your behalf. Attackers industrialized years ago; defenses built for a perimeter era are structurally behind.
The market is responding with a shift from reactive defense to preemptive cybersecurity: predictive threat intelligence, deception, automated response and AI-assisted security operations. Analysts expect preemptive approaches to dominate security spending within the decade. The practical question for most enterprises isn't whether to modernize security — it's how to do it without a blank check or a bigger team.
The Varasun Approach
How we deliver it
01
Assess Exposure
Attack-surface mapping, control-gap analysis and identity review — a clear-eyed picture of real risk.
02
Architect Zero Trust
Identity-centric architecture: verify explicitly, least privilege, assume breach — phased, not forklift.
03
Instrument Detection
Unified telemetry across cloud, endpoints, network and applications feeding a monitored detection layer.
04
Respond & Harden
24/7 SOC operations with automated response playbooks and continuous posture improvement.
Capabilities
What cybersecurity includes
Security Strategy & Assessments
Risk-based roadmaps, posture assessments and board-ready security narratives.
Zero Trust & Identity
Identity-first architecture, privileged access management and conditional access across the estate.
Cloud & AI Security
Cloud workload protection, AI/agent security controls and SaaS security posture management.
Threat Detection & SOC
SIEM/XDR engineering, detection content and 24/7 analyst-led monitoring.
Incident Response & Resilience
Response playbooks, forensic readiness and recovery engineering for ransomware-grade events.
Compliance & Governance
Control mapping, evidence automation and audit readiness across frameworks.
How It Fits Together
Delivery Model
How Varasun actually delivers
01
Phased Zero-Trust Blueprints
Quick wins in weeks, structural change in quarters — each phase independently valuable.
02
Detection-First Engineering
We instrument before we promise — coverage maps show exactly what is watched.
03
Managed Security Operations
Our SOC becomes your SOC: monitoring, triage, response and reporting under one SLA.
Security & Governance
Security for the AI era, not just the perimeter era
AI agents, service accounts and CI/CD identities now outnumber humans in most estates. Our architectures govern machine and AI identities with the same rigor as people — because that's where the breaches are heading.
- Machine, workload & AI-agent identity governance
- AI security controls against prompt injection & data exfiltration
- Automated containment and response playbooks
Managed Operations
A SOC that never blinks
24/7 security monitoring and response from our operations center — detection engineering, triage, containment and monthly threat reporting your leadership can actually read.
- 24/7 SOC monitoring & incident response
- SIEM/XDR management & detection engineering
- Threat intelligence & posture reporting
Business Value
What changes for the business
Risk reduction you can show the board and insurers
Security operations without the hiring war
Compliance evidence generated by operations, not projects
Resilience: incidents contained in minutes, not weeks
FAQs
Questions enterprise buyers ask us
Most breaches happen through owned-but-untuned tooling. We assess what's actually deployed and monitored versus what's licensed — usually the gap is operations and detection content, not products.
Identity becomes the control plane: every access verified, least-privilege by default, segmentation that limits blast radius. We implement it in phases so the business never feels the construction work.
Yes. We operate and improve the stack you have — or rationalize it if it's redundant. The goal is coverage and response quality, not tool replacement for its own sake.
Model and agent access controls, prompt-injection defenses, data-lineage controls and monitoring for anomalous agent behavior — integrated into your SOC so AI incidents follow the same response discipline as everything else.
Explore other capabilities
Start the Conversation
Ready to transform what's possible?
Let's discuss your technology priorities and build a practical path forward — together.